● LIVE DEMO & PORTFOLIO • Target: Tier 1/2 SOC Analyst

Cloud-Native SIEM & Detection Engineering Lab

An enterprise security operations lab built inside Microsoft Azure. Telemetry ingestion via Azure Monitor Agent & Sysmon, real-world adversary simulation (LOLBAS, Credential Access), custom KQL analytics rules mapped to MITRE ATT&CK, and automated SOAR threat enrichment.

SIEM: Microsoft Sentinel Query: KQL (Kusto) Framework: MITRE ATT&CK SOAR: Azure Logic Apps EDR: Microsoft Sysmon

Sentinel Security Incidents Console

Click any incident row below to simulate live analyst triage and review incident telemetry.

Workspace: law-sentinel-soc
Total Incidents (24h)
18 ▲ 4 new today
High Severity Alerts
3 Action required
Mean Time To Triage (MTTT)
4.2 min ▼ 68% via SOAR
Threat Intelligence
AbuseIPDB ● Connected
Severity Incident Title MITRE ATT&CK Offending Entity SOAR Action Details
HIGH High-Volume RDP Brute Force Detection 14 consecutive failed logons (Event 4625) T1110.001 Brute Force 198.51.100.2 (Score 92%) Auto-Enriched & Alerted
HIGH Ingress Tool Transfer via Certutil (LOLBAS) certutil.exe -urlcache -split (Sysmon Event 1) T1105 Ingress Transfer User: AdminUser (PID 4892) Hash Logged
MED Unauthorized Local Administrator Account Creation User: SOCBackdoorUser escalated (Events 4720 & 4732) T1136.001 Local Account Target: SOCBackdoorUser Escalated to Tier 2
HIGH Suspicious Encoded / Hidden PowerShell Command flags: -enc -w hidden -ep bypass T1027 Defense Evasion powershell.exe Closed (Remediated)

Evidence & Visual Telemetry

Full visual evidence of Sentinel incidents, KQL query results, threat maps, and SOAR execution flows.

1. Microsoft Sentinel Incident Queue Dashboard
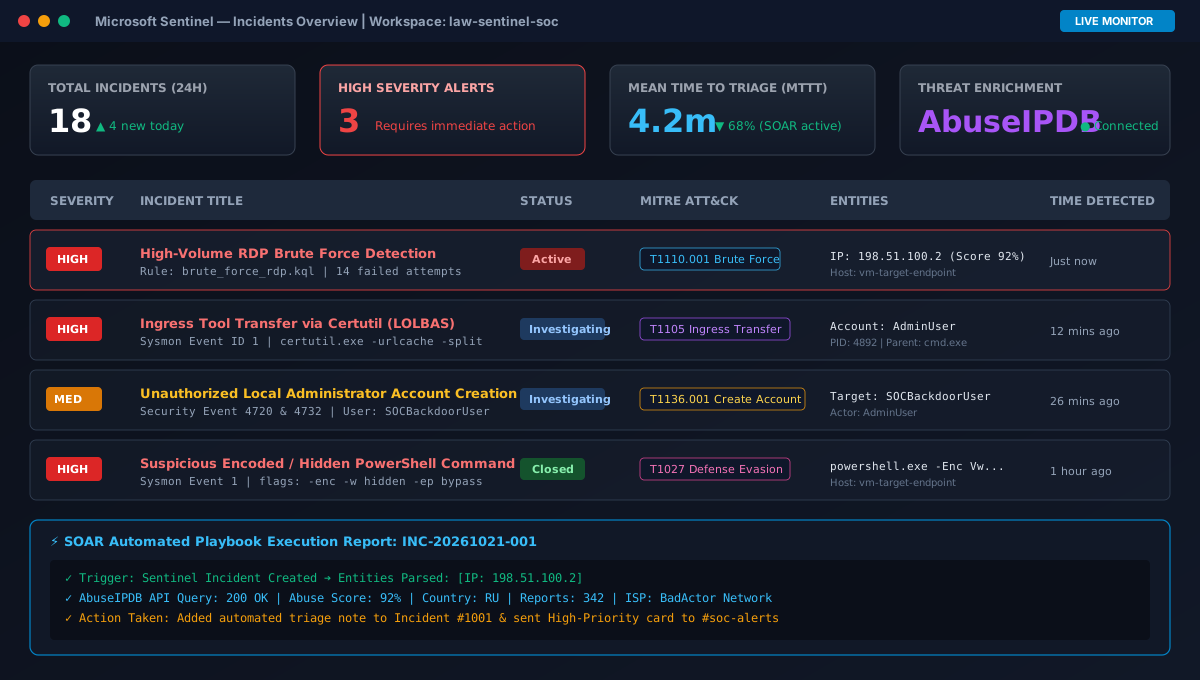
Sentinel Incident Dashboard
2. KQL Query Investigation & Results Log Analytics
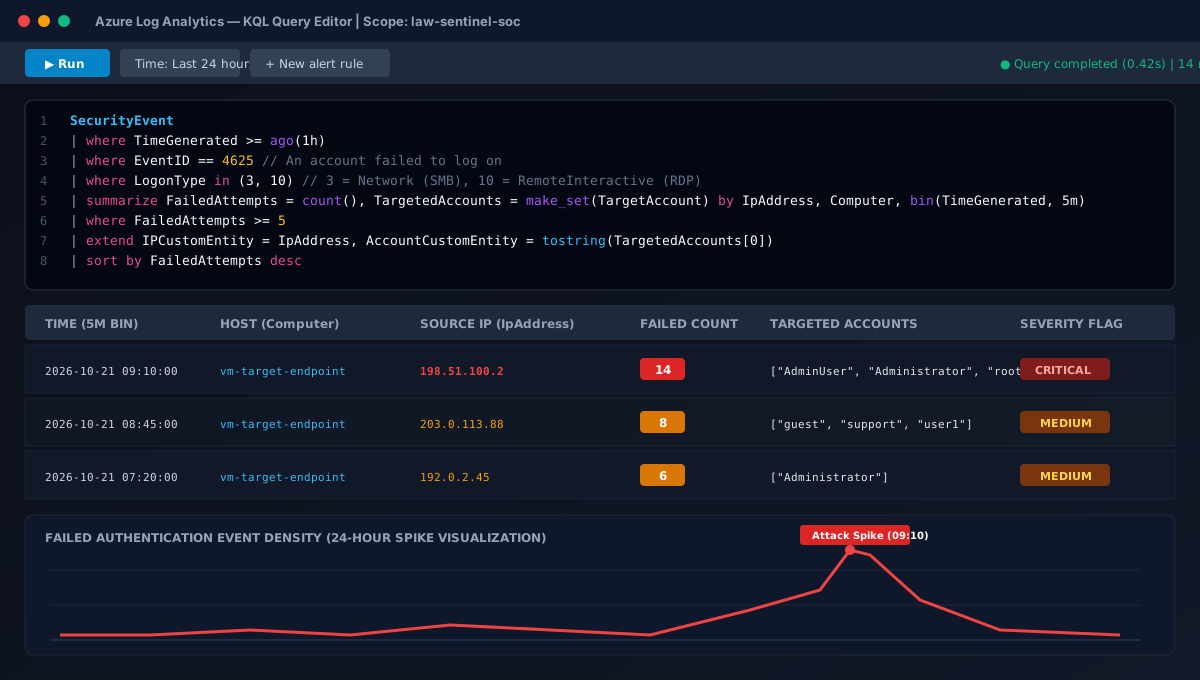
KQL Query Investigation
3. Global Threat Geolocation Workbook Azure Maps
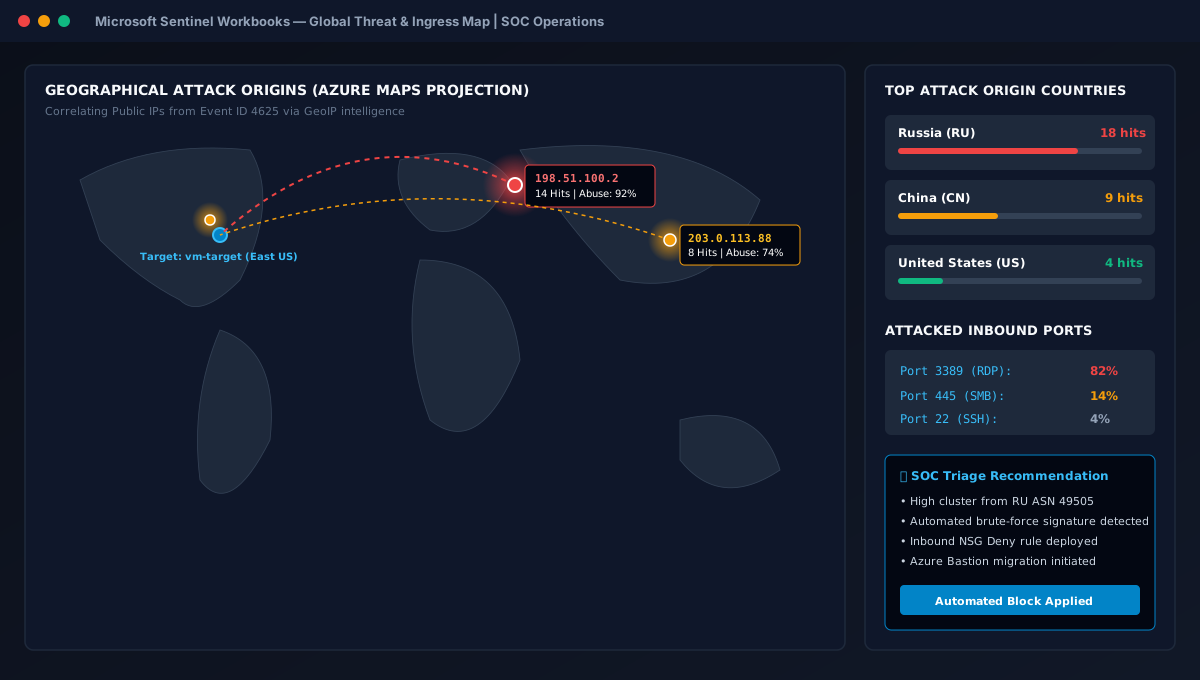
Global Threat Map
4. Logic App SOAR Automation Run Logic Apps
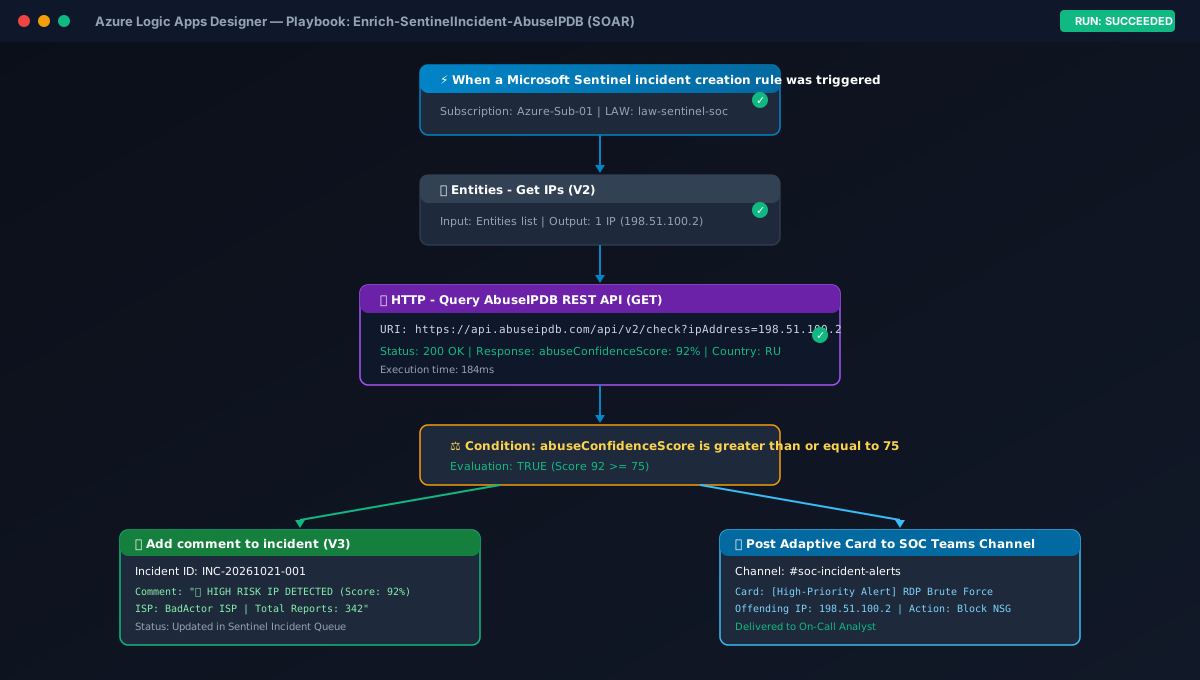
Logic App SOAR Automation

Production KQL Analytics Rules

Inspect the exact detection engineering logic authored for Microsoft Sentinel.

T1110.001 - High-Volume RDP Brute Force Detection
SecurityEvent
| where TimeGenerated >= ago(1h)
| where EventID == 4625 // An account failed to log on
| where LogonType in (3, 10) // 3 = Network (SMB), 10 = RemoteInteractive (RDP)
| where isnotempty(IpAddress) and IpAddress !in ("-", "127.0.0.1", "::1")
| summarize 
    FailedAttempts = count(),
    StartTime = min(TimeGenerated),
    EndTime = max(TimeGenerated),
    TargetedAccounts = make_set(TargetAccount, 10),
    SubStatusList = make_set(SubStatus, 5)
    by Computer, IpAddress, bin(TimeGenerated, 5m)
| where FailedAttempts >= 5
| extend 
    AccountCustomEntity = tostring(TargetedAccounts[0]),
    IPCustomEntity = IpAddress,
    HostCustomEntity = Computer
| project StartTime, EndTime, HostCustomEntity, IPCustomEntity, AccountCustomEntity, FailedAttempts, TargetedAccounts, SubStatusList
| sort by FailedAttempts desc

Standardized SOC Incident Report

Demonstrating enterprise incident response documentation and root-cause analysis.

INCIDENT ID INC-20261021-001
SEVERITY HIGH
STATUS CLOSED (CONTAINED)
ATTACKER IP 198.51.100.2 (92% Abuse)

1. Executive Summary

On October 21, 2026, Microsoft Sentinel alerted on anomalous brute-force authentication against vm-target-endpoint. Subsequent investigation confirmed successful credential guessing against account AdminUser, followed by secondary stage ingress via certutil.exe and local administrative persistence via rogue account SOCBackdoorUser. Attacker was isolated, rogue account purged, and perimeter NSG rule enforced.

2. Attack Chain Timeline (UTC)

09:10:15 WinSec Event 4625: 14 failed RDP authentication attempts from source 198.51.100.2.
09:13:02 WinSec Event 4624: Successful RDP logon for user AdminUser from attacker IP.
09:15:40 Sysmon Event 1: certutil.exe -urlcache -split executed to fetch external binary.
09:17:15 WinSec Event 4732: Rogue user SOCBackdoorUser added to local Administrators group.

3. Remediation & Hardening Implemented

  • Perimeter Containment: Added Azure NSG Inbound Deny Rule for 198.51.100.2.
  • Identity Remediation: Forced password rotation for AdminUser and purged SOCBackdoorUser.
  • Zero Trust Hardening: Disabled direct public RDP Port 3389; migrated access to Azure Bastion.